Technology and security leadership for companies that answer to regulators.
Fractional CISO and CTO for medical device, healthcare, legal, and financial services companies. I own the architecture and the security program, so they stop fighting each other.
I came to security from engineering, not from compliance, and that’s the difference.
Which problem is in front of you?
Most companies need one of these more urgently than the other. Plenty eventually need both, and one person holding both is usually cheaper and faster than two who have to agree with each other.
Fractional CISO
Own the security program, not a folder of policies.
Risk register, vendor risk, regulator and auditor response, board and customer reporting.
FDA device cybersecurity, penetration test remediation, and the architecture work after an incident.
AI governance: what staff are already using, on what data, under whose agreement.
What a fractional CISO covers →Fractional CTO
Own the architecture and the roadmap.
Build versus buy, cloud cost and posture, vendor and team oversight.
Technical due diligence, and deciding which problems genuinely need a model at all.
What a fractional CTO covers →Bring your FDA letter, pen test report, audit deadline, or architecture problem. You'll talk to me, not a sales rep.
Not ready for a call? Send a message instead.
For companies looking to engage BATO. Vendors, please email.
Regulated companies, where the evidence gets read
The common thread is not company size. It is that somebody outside the building will eventually read what you wrote down, and be in a position to do something about it.
Medical device and SaMD
Premarket cybersecurity under Section 524B, deficiency letters with a 180-day clock, threat models and testable security requirements, and penetration testing evidence a reviewer can follow.
Medical device and SaMD →Digital health and healthcare IT
HIPAA Security Rule obligations that have to survive an enterprise customer reading them, plus the architecture underneath: tenant separation, authorization on every request, and audit logging that exists before somebody asks for it.
Digital health and healthcare IT →Legal
Client confidentiality obligations that read like a security program once you write them down, matter and document systems that grew organically, and the diligence questionnaires that arrive with every large client.
Legal →Financial services
Platform migrations that cannot drop transactions, examiner and auditor expectations, and a technology roadmap a board will actually sign off on.
Financial services →Three steps, and a price you can plan against
Intro call
Thirty minutes. You tell me what is going on, I tell you what it involves and whether you need me at all. If the honest answer is that you can do this in-house or that you need a different specialist, you get that answer here rather than in the third invoice.
Scoped proposal
A written scope naming which responsibilities are mine, what arrives on what cadence, and what I am accountable for producing. A monthly fee for unspecified availability is how these arrangements quietly turn into nothing, so the scope is the product.
Monthly retainer or fixed-bid project
Ongoing ownership runs as a retainer, and retainers start at $5,000/month. Work with a defined finish line runs fixed-bid with milestones and an end date. Everything I build, document and configure is yours either way.
The longer version, including what each phase produces and how the two models differ, is on how I work.
Bring your FDA letter, pen test report, audit deadline, or architecture problem. You'll talk to me, not a sales rep.
Not ready for a call? Send a message instead.
For companies looking to engage BATO. Vendors, please email.
Case Studies
Real problems, real solutions. Here's what it looks like when I get involved.
FDA 510(k) Cybersecurity Remediation
Cybersecurity remediation carried through to FDA 510(k) clearance. Audited submission security claims against the shipped product and reconciled the documentation to as-built behavior.
Read the case study →EMR Platform Migration from Legacy Java to Azure
Fully modernized EMR platform running on Azure with automated deployments, HL7/FHIR integrations, and a scalable architecture the team could maintain independently.
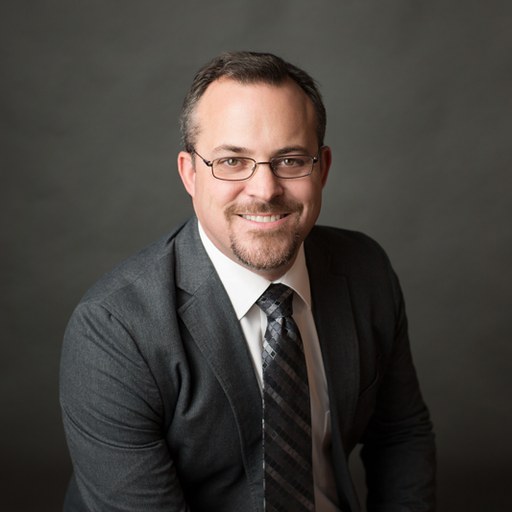
Read the case study →Bill Barksdale
I co-founded AccuConference, grew it to 10,000+ customers, and sold it to NTT. I stayed six years and rose to CTIO, running a technology organization of 225+ people across 8 countries on a $33M budget, reporting to the board, the parent company board, and executive leadership. After that I joined a healthcare workforce startup as employee #5, rebuilt the engineering organization to 40+, and helped lead the company through acquisition. Two exits, and over 20 years of this.
Then I worked out something about myself. I am not a sit-in-meetings executive. I lead by owning the architecture and the security program, and by still being able to open either one and check that it says what everybody believes it says.
Now I run a boutique consulting practice, and the work is owning one of two things: the security program, or the architecture. A medical device heading into an FDA submission that needs a cybersecurity package. A penetration test report full of findings and nobody who can close them. An environment that needs its architecture and identity layer rebuilt after an incident has been contained. A platform that has outgrown the architecture it started on, with a roadmap nobody senior has pressure-tested. Healthcare, medical devices, legal, financial services: regulated industries, where the consequences are real.
I can read the finding, write the fix, and produce documentation that holds up for a regulator, rather than hand you a report and a list of recommendations someone else has to implement. CISSP certified.
I don't sell hours. Ongoing leadership runs as a monthly retainer with named responsibilities, starting at $5,000/month. Work with a defined finish line runs fixed-bid, with a scope, milestones and an end date. Either way you know what you are buying before it starts, and there is no open-ended billing.
Questions buyers ask first
What does a fractional CISO or CTO actually do?
Owns a function rather than advising on one. As a fractional CISO that means the security program: the risk register, the policies, vendor risk, the answers that go back to regulators, auditors and enterprise customers, and the reporting that reaches your board. As a fractional CTO it means the architecture and the technology roadmap: what gets built, what gets bought, what the cloud estate costs and exposes.
How is this different from hiring someone full-time?
Cost and fit. The rule I use is that a full-time hire makes sense once there is enough work in one specialization to keep one person genuinely busy. Below that line you are paying a full salary for a part-time load, and in a regulated company that load is usually spread across four specializations rather than concentrated in one. When any of them becomes a full week of work, I will tell you to hire for it.
What does it cost?
Retainers start at $5,000 a month. Where an engagement lands above that depends on how much estate there is and how much of it is urgent. Work with a defined finish line, such as a deficiency letter response or a penetration test remediation, is quoted fixed-bid instead. I do not sell hours.
Which industries do you work in?
Regulated ones, where getting it wrong is expensive in a way that is written down somewhere: medical device and SaMD companies, digital health and healthcare IT, legal, and financial services. The common thread is that somebody outside the company will eventually read your evidence.
Do you do incident response?
No. If you are in an active incident, call a specialist response firm, and do it before you call me. What I do is the part afterwards: once containment is done and the responders have gone, the architecture, the identity layer and the applications still contain the path that was used, and closing it is engineering work that somebody has to own.
Do you handle AI governance?
Yes, the governance, data protection and vendor side of it: finding what staff are already using, an acceptable use policy people will follow, business associate agreements and processing terms, and a route to approving new use cases. Not model development, machine learning research or data science, which are different disciplines and a different hire.
Do you work remotely?
Yes, and most engagements run that way. I am based in Nolensville, Tennessee, just outside Nashville, so Middle Tennessee companies get on-site time easily. Everywhere else in the US is remote with travel when something genuinely needs a room.
What’s in front of you?
Tell me what’s going on. You’ll hear back from me directly, with a straight answer on whether I’m the right fit.
Rather skip the form? bill@bato.com reaches me directly.
Submissions are processed by Web3Forms. I use what you send only to respond to your inquiry. See the privacy policy.